Security
ENTERPRISE-GRADE SECURITY AND CONTROLS.
SOC 2 Type II compliant. ISO 27001 certified. GDPR compliant. Customer environments are isolated, operations are traceable and your data never trains our models.
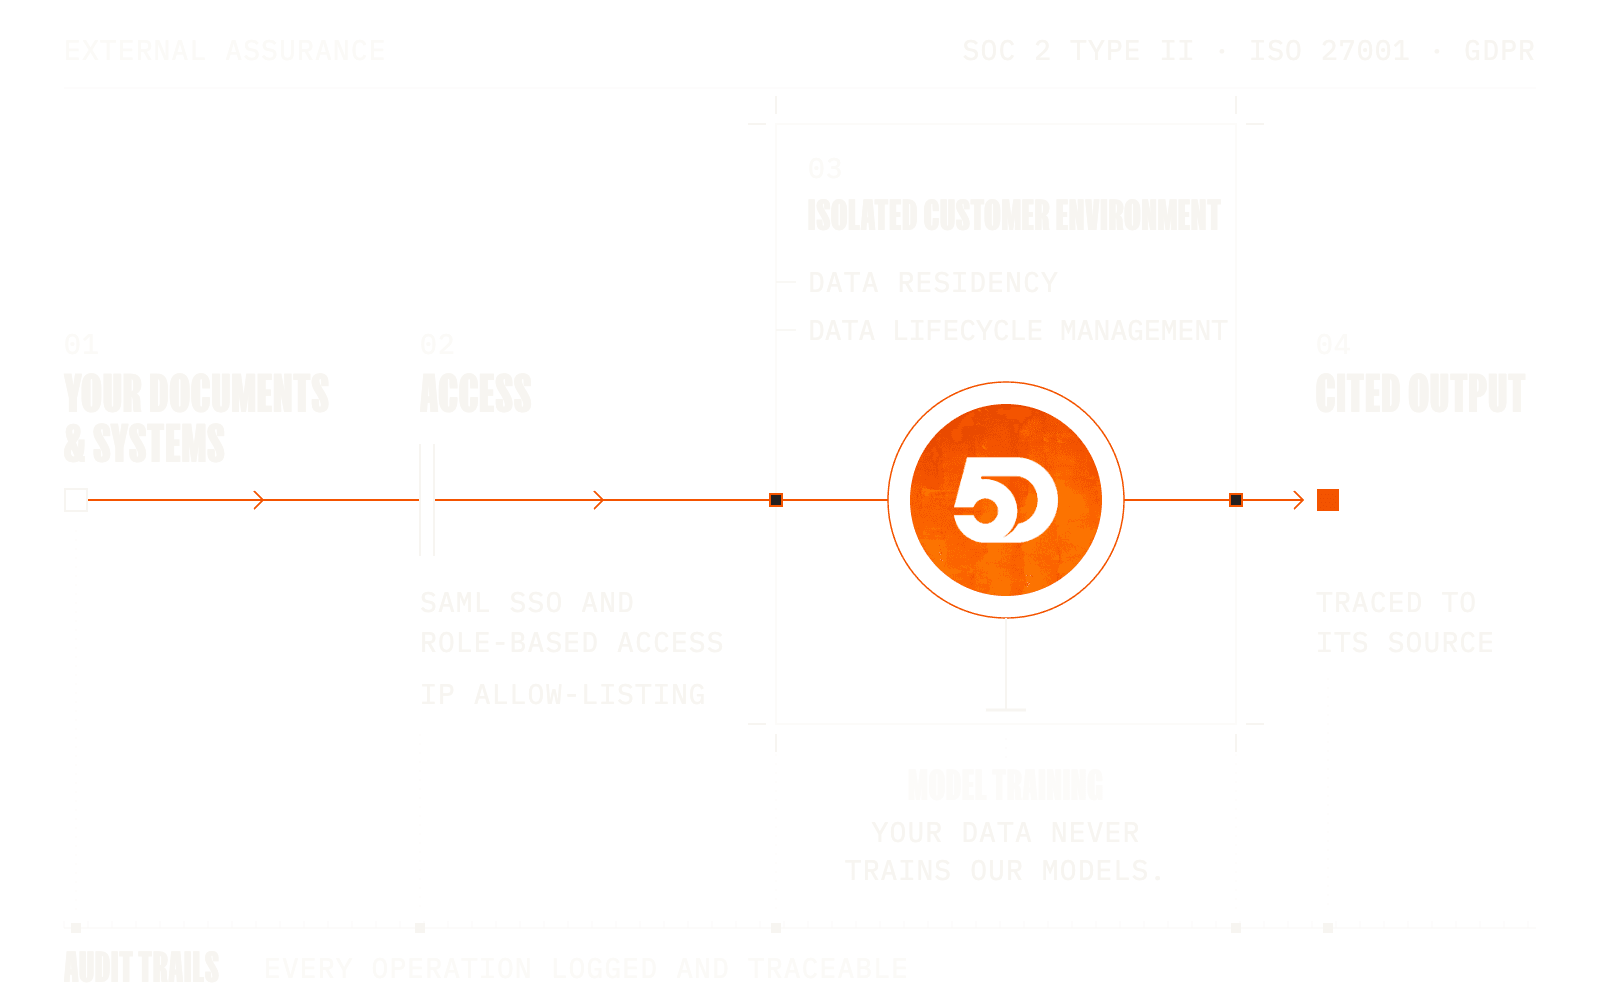
EXTERNAL ASSURANCE.
Independent standards and regulatory commitments provide a clear foundation for security and data protection.
SOC 2 Type II
Security practices meet institutional requirements for security, availability, processing integrity, confidentiality and privacy.
ISO 27001
One of the highest international standards for information security and the systematic management of sensitive company and customer information.
GDPR
Full compliance with European data-protection regulation. EU data stays in the EU and US data stays in the US.
CONTROLS BUILT INTO THE PLATFORM.
Security is part of how Fifth Dimension handles every customer, user and operation, not a layer added after the work is done.
Your data never trains our models.
Customer data remains private and is never used to train the models that power Fifth Dimension.
Customer isolation
Each customer operates in a separate product environment, with no data cross-pollination between clients.
Audit trails
Every operation is logged and traceable, giving compliance teams visibility into how work was completed.
Data residency
Keep customer data within the region agreed for your deployment.
On-premise deployment
Available for firms that require on-premise or air-gapped environments.
SAML SSO and role-based access
Centralise identity and control access by role so each person can reach only the work and information they need.
IP allow-listing
Restrict platform access to approved networks and IP addresses.
Data lifecycle management
Apply agreed controls to how customer data is retained and removed throughout its lifecycle.
GIVE YOUR SECURITY TEAM THE DETAIL.
Review Fifth Dimension's security, privacy and data-handling documentation in the Trust Centre.
Visit the Trust Centre